NSA/CSS EPL-listed
Garner TS-1XTE
Erases hard drives and tapes in 15 seconds. Includes SCAN-1X logging for every cycle.
- Field
- 2.0 T (20 000 G)
- Capacity
- 150 × 3.5″ per hour
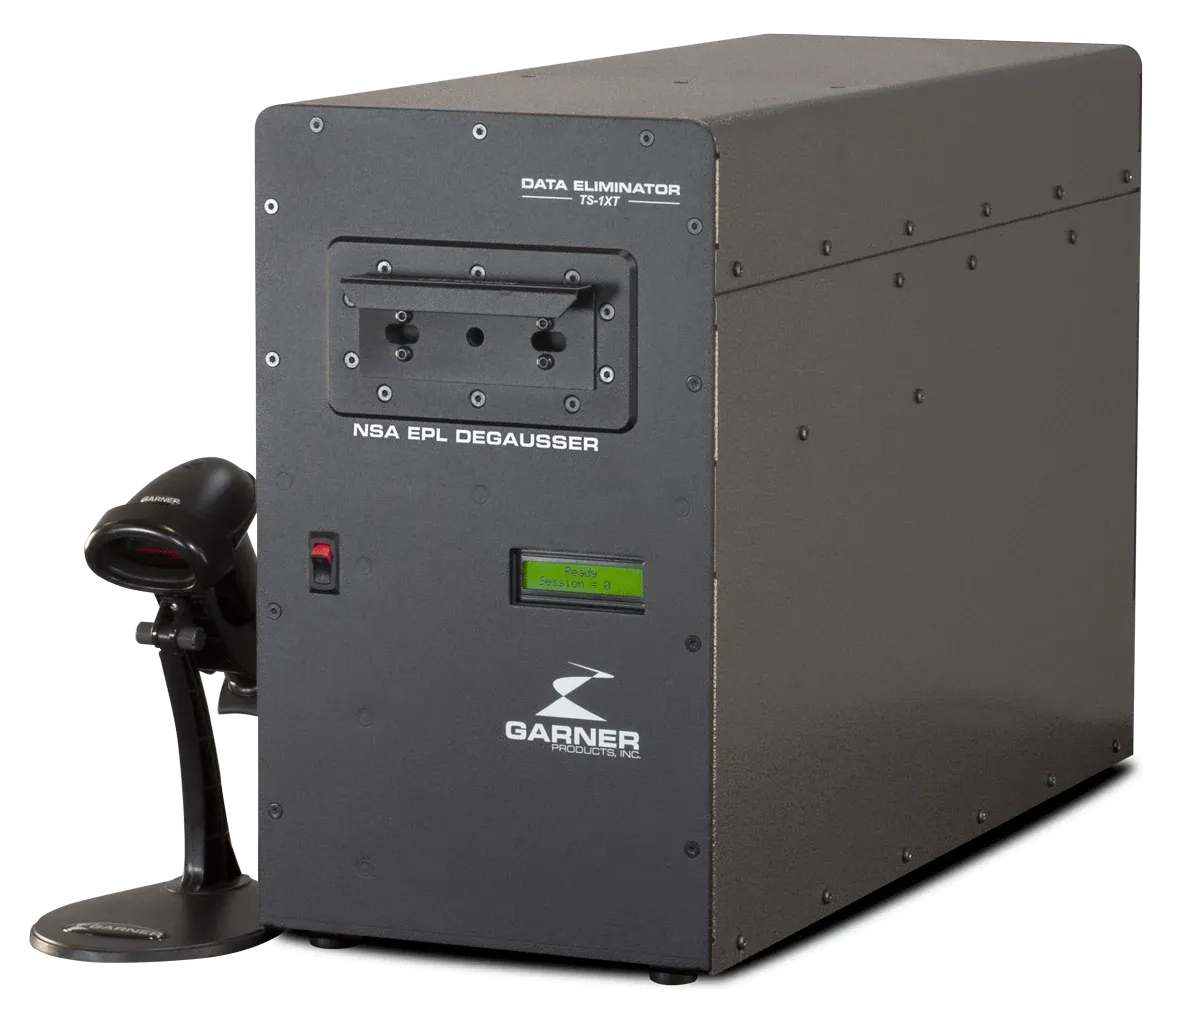 DegaussersErase magnetic media with a strong magnetic field.5 models
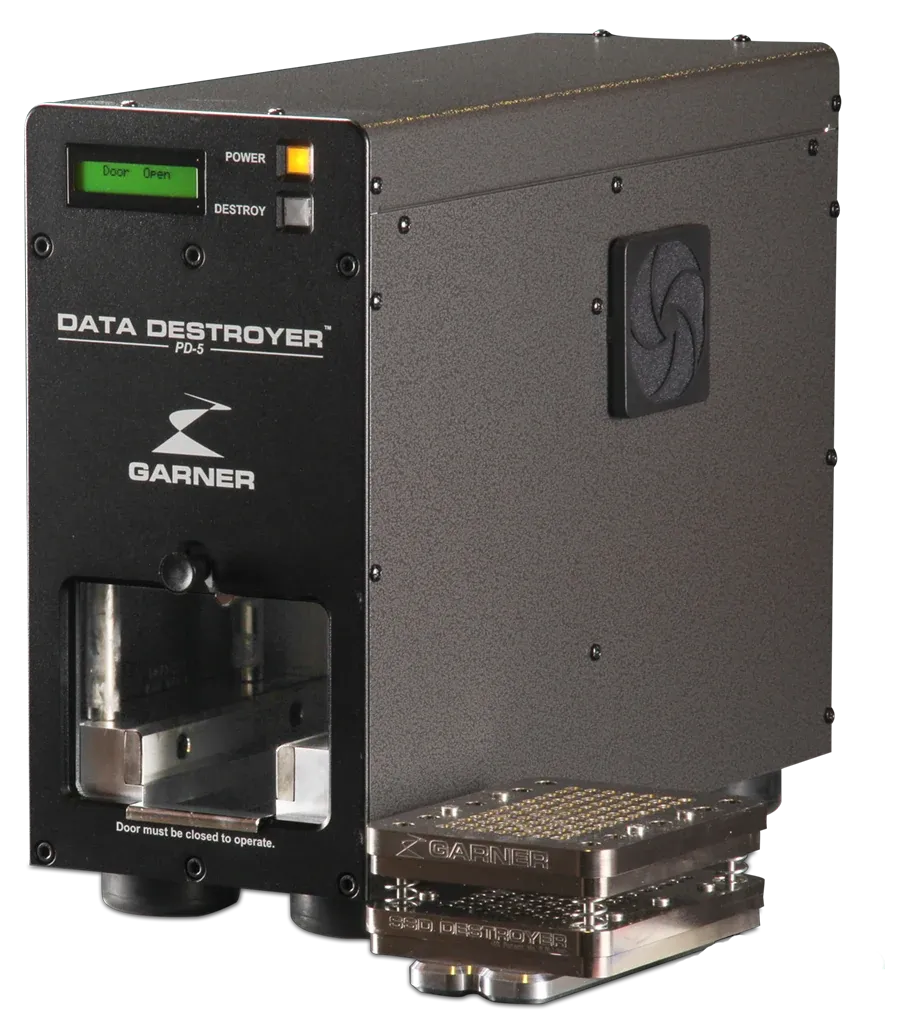 DestroyersPhysically deform hard drives and SSDs.2 models
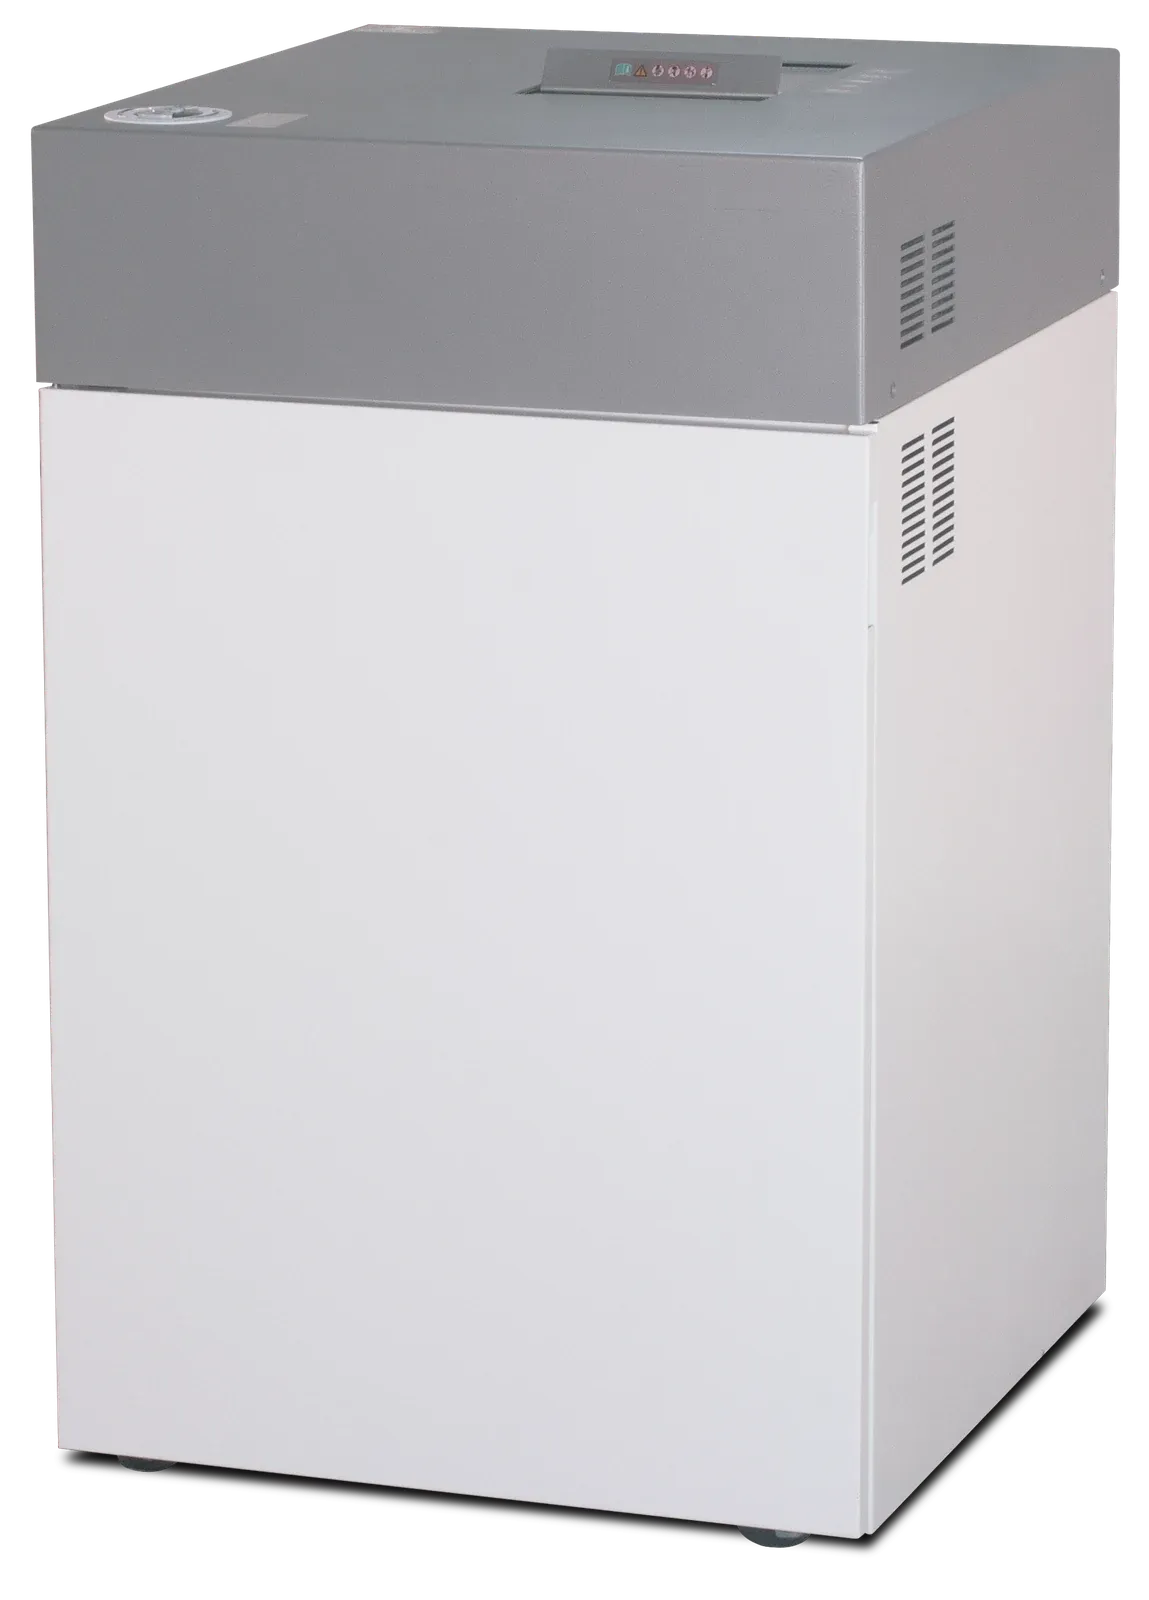 ShreddersShred flash memory, SSDs and small media.1 model
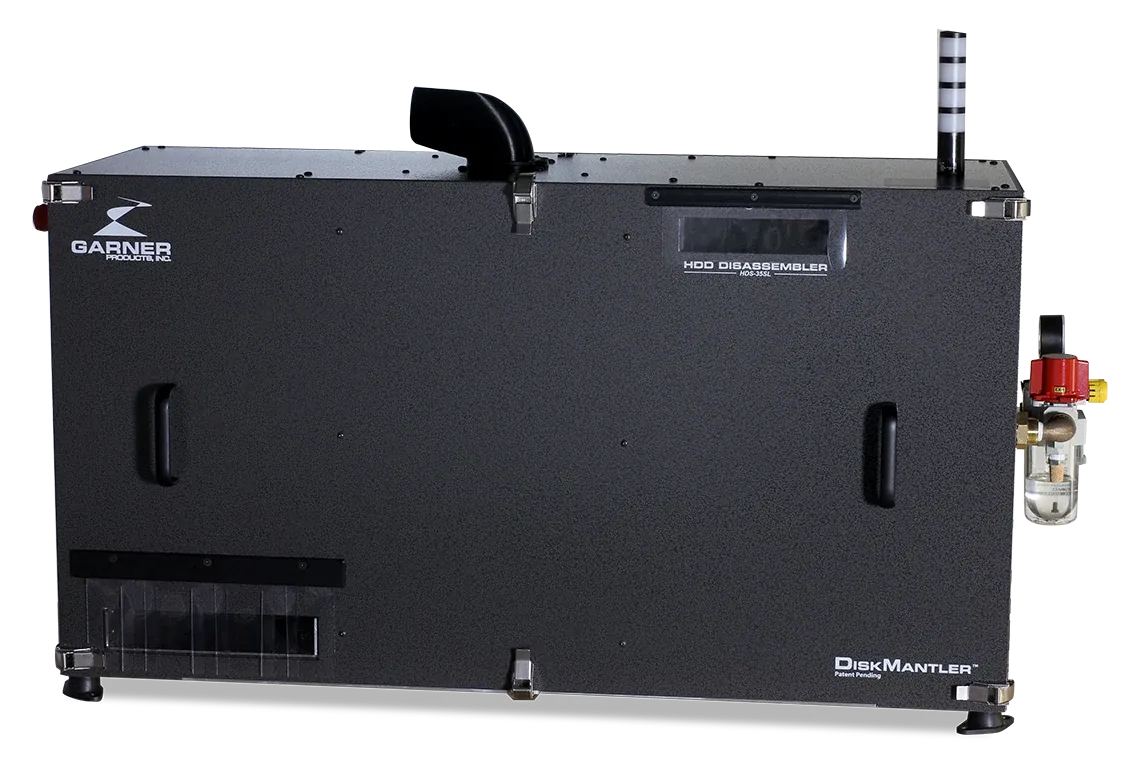 DiskMantlersDismantle hard drives into separate components.3 models
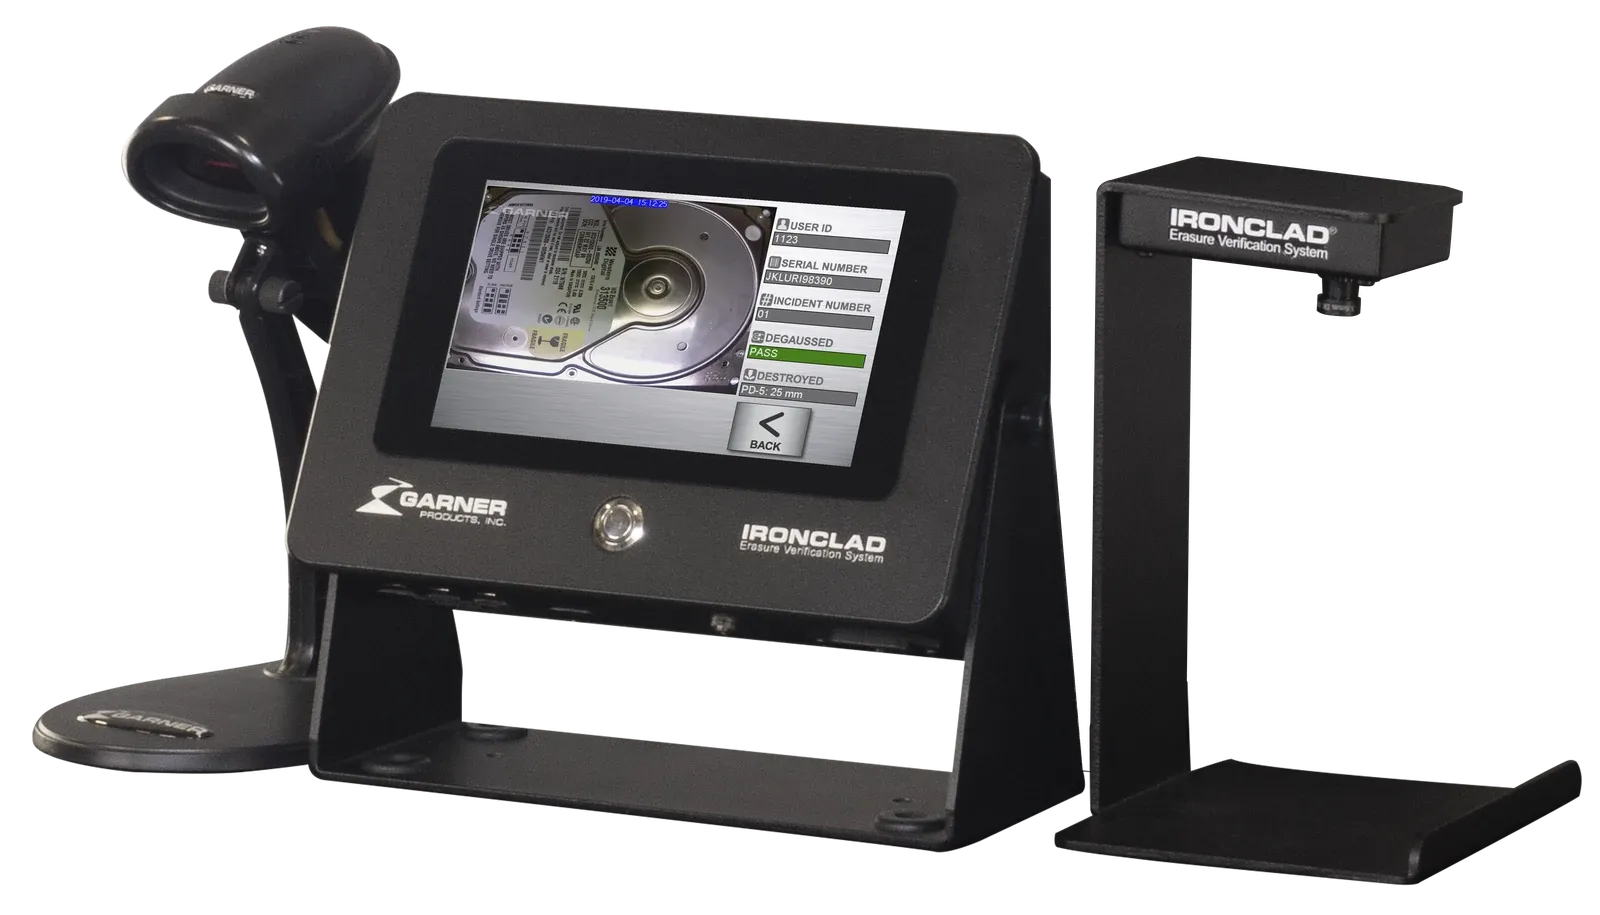 VerificationRecord and prove every erased or destroyed drive.1 model
Industry
Banks, insurers and payment companies retire devices that hold customer and transaction data. Auditors and supervisors expect a documented, verifiable disposal process.
The GDPR applies to customer data, and financial institutions are also supervised on their information security and IT risk management. Card data falls under PCI DSS, which requires secure deletion of cardholder data that is no longer needed. Institutions with US activities meet the Safeguards Rule under the Gramm-Leach-Bliley Act (GLBA), which requires procedures for the secure disposal of customer information.
What these frameworks have in common: a written procedure, a method that fits the media, and evidence per device.
Overwriting software is suitable when devices are reused. When a device leaves the organisation for good, many institutions choose physical destruction, often after degaussing hard drives. For SSDs and phones, a shredder or the PD-5E with SSD-1E applies.
IRONCLAD records each item with serial number, operator, witness, result and photo, and exports certificates and spreadsheets for your audit file.
Erases hard drives and tapes in 15 seconds. Includes SCAN-1X logging for every cycle.
Bends and breaks hard drives with more than 10 tons of force in under 20 seconds. NSA/CSS EPL-listed.
Shreds SSDs, USB sticks, phones and optical discs into particles of 4 × 15 mm.
Photo, pass/fail result and certificate per drive. For Garner degaussers, destroyers and the FLASHPRO, or stand-alone.
We help you combine destruction and verification in one workflow.